
Eighty percent of large financial institutions now run AI inside core compliance functions. Fewer than 12% have the governance infrastructure to defend what that AI is doing when a regulator asks. This whitepaper names the gap, automated compliance volume versus compliance assurance, and shows exactly where it breaks: AML monitoring that can’t produce a SAR-ready explanation, credit models that pass accuracy tests but fail adverse action requests, regulatory reports built on data no one can reconstruct. Inside: the consent order that cost 18 months and could have been avoided with six weeks of engineering, and the five-stage resilience framework built for AI, not the audit cycle.
Key themes covered:
- Why 80% AI adoption and 12% governance readiness is the real compliance risk, not the tech itself
- Determination-level explainability: what SAR filings require that AI-generated alerts don’t automatically produce
- The adverse action trap: why institutions get penalized for undocumented reasons, not wrong decisions
- Fair lending exposure hidden in unstructured text your standard bias testing never sees
- The shadow AI problem in regulatory reporting, and why “we didn’t know the team was using it” isn’t a defense
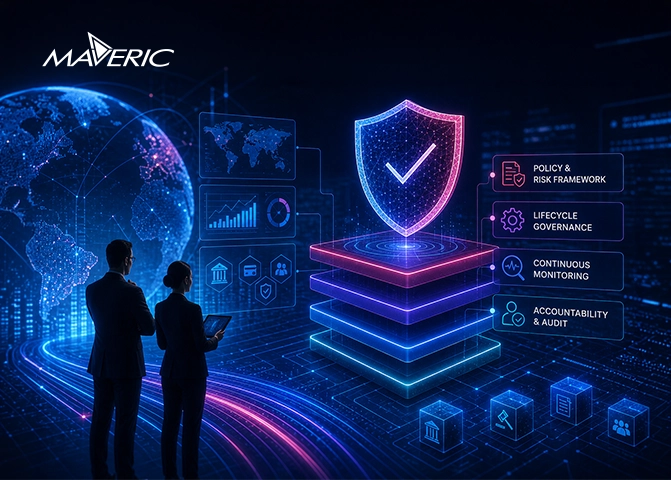
- Predict-Prevent-Mitigate-Recover-Restore, rebuilt for the model level instead of the programme level